Acadia Healthcare Breach Exposes Patient Data, Including Some SSNs
Acadia Healthcare, one of the largest behavioral health providers in the country, confirmed a data breach that exposed sensitive patient information. For some patients, that included a Medicare number that may contain their Social Security number. The breach started with a social engineering attack, a scam that tricks a person into giving up access.
It hit one employee's email and SharePoint account between March 21 and 25, 2026. Acadia mailed notification letters to 1,807 people on May 22, 2026.
If you work in behavioral health, this one hits close to home. Acadia is not some small clinic that skipped a firewall update. They are a major player with resources, and they still got caught. That should make every practice owner pause.
What Data Was Exposed and Who Is Affected
The exposed data included names, addresses, dates of birth, treatment details, and health insurance information. Some patients also had a Medicare number exposed that may contain their SSN. An exposed SSN is about as bad as it gets. An SSN is yours for life; you cannot change it like a password. Acadia reported that the intruder did not reach any other email accounts, other systems, or its electronic medical record system.
Acadia mailed breach notification letters to affected individuals on May 22, 2026, under the Breach Notification Rule (45 CFR §§ 164.400 to 164.414). If you receive one, take it seriously. Freeze your credit, monitor your accounts, and do not ignore it.
Who Must Be Notified After a Breach, and When
The Breach Notification Rule sets a different audience and deadline depending on how many people a breach of unsecured PHI touches:
| Who gets notified | When it applies | Deadline | Rule |
|---|---|---|---|
| Affected individuals | Every breach of unsecured PHI | Without unreasonable delay and in no case later than 60 calendar days after discovery | 45 CFR 164.404(b) |
| Prominent media outlets | More than 500 residents of a State or jurisdiction | Without unreasonable delay and in no case later than 60 calendar days after discovery | 45 CFR 164.406 |
| HHS (the Secretary) | 500 or more individuals | At the same time as the notices to individuals | 45 CFR 164.408(b) |
| HHS (the Secretary) | Fewer than 500 individuals | Kept in a breach log, then reported not later than 60 days after the end of the calendar year | 45 CFR 164.408(c) |
Acadia's letters went to 1,807 people, which puts this breach in the 500-or-more row for reporting to HHS.
Key Terms Defined
- Protected Health Information (PHI): Individually identifiable health information held or transmitted by a covered entity or business associate, in any form or medium. A patient's Social Security number sitting in a treatment or billing record is PHI (45 CFR 160.103).
- Breach: The acquisition, access, use, or disclosure of PHI in a manner not permitted under the Privacy Rule which compromises the security or privacy of that PHI. An impermissible use or disclosure is presumed to be a breach unless a documented risk assessment shows a low probability that the PHI was compromised (45 CFR 164.402).
- Unsecured PHI: PHI that has not been rendered unusable, unreadable, or indecipherable to unauthorized persons, for example through encryption that meets HHS guidance (45 CFR 164.402). Only a breach of unsecured PHI triggers the notification duties below.
- Breach Notification Rule: After a breach of unsecured PHI is discovered, affected individuals must be notified without unreasonable delay and no later than 60 calendar days, HHS must be notified, and breaches involving more than 500 residents of a state require media notice (45 CFR 164.400 to 164.414).
HIPAA Compliance Failures Behind the Breach
Acadia's investigation traced the breach to one employee account that an outsider got into. That points to gaps under the HIPAA Security Rule. If an outsider gets into an account that holds PHI (protected health information), something failed. It could be access controls, monitoring, staff training, or a mix of them.
Training is not optional under the Security Rule. The standard reads:
“Implement a security awareness and training program for all members of its workforce (including management).”
A social engineering attack is aimed squarely at that workforce, which is why phishing practice belongs in the training, not just a policy binder.
The Privacy Rule requires covered entities to make reasonable efforts to use, share, or request only the minimum necessary protected health information for the purpose at hand (45 CFR § 164.502(b)). When SSNs sit in an employee's email and shared files, one stolen login is enough to break that protection. A thorough security risk assessment would likely have identified these vulnerabilities before an attacker did.
In my experience, behavioral health organizations often lag behind hospitals in security maturity. The clinical focus is intense, and IT security gets treated as overhead. That is exactly how breaches like this happen.
Lessons for Small and Mid-Size Practices
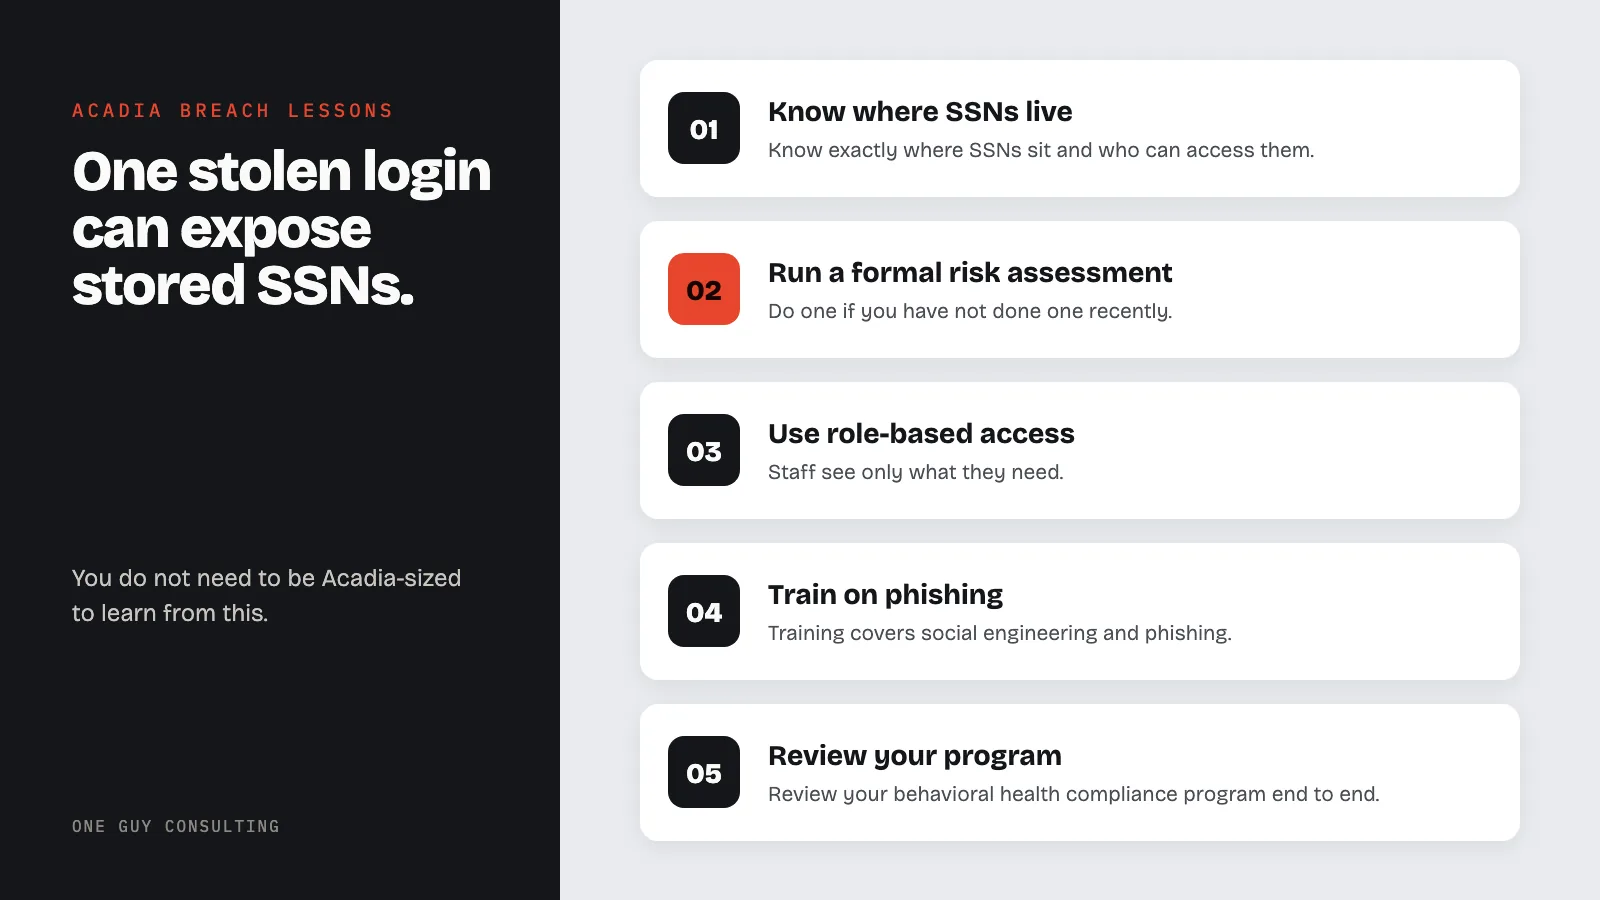
You do not need to be Acadia-sized to learn from this. If your practice stores SSNs, you need to know exactly where they live in your systems and who can access them. In many small practices, SSNs end up scattered across intake forms, billing systems, email, and sometimes even shared spreadsheets.
Start with the basics:
- Conduct a formal risk assessment if you have not done one recently
- Implement role-based access controls so staff only see what they need
- Ensure your workforce training covers social engineering and phishing
- Review your behavioral health compliance program end to end
Breaches like Acadia's are a reminder that compliance is not a checkbox exercise. It is an ongoing process that requires attention, resources, and honest self-assessment.
I have seen what that work looks like up close. In Case 01, a Florida mental health franchise office had policies that were never written, records with holes, training half done, and a state auditor due in days. It went from that to audit-ready in under a week, and it passed its state audit. In Case 05, a single-location practice had several vendors handling PHI with no BAA (business associate agreement, the contract HIPAA requires before a vendor handles PHI for you). Every missing BAA got signed, and the practice now has a repeatable vendor review.
Key stat: Healthcare data breaches affecting 500 or more individuals must be reported to HHS at the same time individuals are notified, no later than 60 calendar days after discovery (45 CFR § 164.408(b), § 164.404(b)). Each breach triggers mandatory notification to affected individuals, HHS, and in some cases the media, which is why preventing a breach beats responding to one.
One Guy Consulting in 37 seconds
Breach News and Analysis
- Healthcare Breaches Doubled in 2025: Full Analysis
- Healthcare Data Breach Trends Analyzed
- Okanogan Breach Settlement
- UMMC Ransomware Attack Lessons
Related Reading
- How to Respond to a HIPAA Data Breach
- Healthcare Data Breach Prevention Strategy
- Breach Notification Requirements and Timelines
- Healthcare Breaches Doubled in 2025
- $6.6M in HIPAA Fines in 2025
- Change Healthcare Breach: One Year Later
For more on how vendor relationships create compliance exposure, see our coverage of the Telnyx supply chain breach and the Vercel security incident.
Sources
Try three One Guy Consulting 3D staff training courses free →
Frequently Asked Questions
What happened in the Acadia Healthcare data breach?
Acadia Healthcare, a behavioral health and substance use disorder treatment provider, reported a social engineering attack, a scam that tricks a person into giving up access. It let an unauthorized person into one employee's email account and SharePoint files between March 21 and 25, 2026. Exposed data included names, addresses, dates of birth, treatment details, and health insurance information. For some patients, it also included a Medicare number that may contain their Social Security number. Acadia mailed notification letters to 1,807 people on May 22, 2026.
Are behavioral health records subject to extra protections beyond HIPAA?
Yes. Substance use disorder treatment records at federally assisted programs are protected by 42 CFR Part 2, which imposes stricter consent and disclosure requirements than the HIPAA Privacy Rule.
What should patients do if their information was exposed in a healthcare data breach?
Patients should monitor their credit reports and explanation of benefits statements for unusual activity, place a fraud alert or credit freeze if Social Security numbers were exposed, and review the breach notification carefully.
What obligations does a covered entity have after a breach?
Covered entities must notify affected individuals without unreasonable delay and no later than 60 calendar days after discovery. They must also notify HHS. If a breach involves more than 500 residents of a state or jurisdiction, they must also notify prominent media outlets.