By Chuck Weiselberg, Founder, One Guy Consulting. Published .
Chuck Weiselberg, Certified HIPAA Professional (CHP); 10 years of HIPAA compliance experience. See author bio: oneguyconsulting.com/author/chuck-weiselberg
HIPAA compliance requirements in New Jersey: practices must follow all of HIPAA (the federal health privacy law), plus state law on top. The biggest addition is the breach law, N.J.S.A. 56:8-163. After a breach, report it to the State Police before you tell patients. Then tell patients as fast as you reasonably can. Separate state rules cover shredding old records and handling Social Security numbers.
A practice manager in Bergen County gets the call every compliance consultant dreads: a billing laptop is missing, it was not encrypted, and it held a spreadsheet with patient names and Social Security numbers. The federal clock starts. What most New Jersey offices do not know is that a second clock starts at the same moment, and that one puts the State Police first in line.
Federal enforcement in the state is real. OCR (the HHS Office for Civil Rights) fined a New Jersey nursing facility $100,000 (a civil money penalty) for being too slow to give patients their records (final determination issued January 12, 2024), and reached an agreement with a New Jersey health care provider that disclosed patient information in response to negative online reviews (June 5, 2023).
This guide covers the federal floor, the New Jersey statutes that stack on top of it, the two breach clocks, the penalties on each side, and what it all means for hospitals, dental offices, behavioral health practices, and home health agencies.
Who must comply in New Jersey
HIPAA (the Health Insurance Portability and Accountability Act) sets a national floor, not a ceiling. 45 CFR 160.203 states the general rule: a HIPAA standard "that is contrary to a provision of State law preempts the provision of State law," and then lists the exceptions. The one that matters most for practices is paragraph (b): state law survives when it "relates to the privacy of individually identifiable health information and is more stringent than" the federal Privacy Rule.
In plain words: where New Jersey is stricter, New Jersey wins. Where HIPAA is stricter, HIPAA wins. A New Jersey covered entity has to satisfy both at once, and the state has not written a HIPAA carve-out into its breach statute.
Who Is a Covered Entity in New Jersey
The definition is federal and does not change at the state line. 45 CFR 160.103 defines a covered entity (a health care provider, health plan or clearinghouse that HIPAA covers) as "(1) A health plan. (2) A health care clearinghouse. (3) A health care provider who transmits any health information in electronic form in connection with a transaction covered by this subchapter." In New Jersey that sweeps in hospitals, physician groups, dental and behavioral health practices, pharmacies, home health agencies, nursing facilities, and any solo practitioner who bills insurance electronically. CMS (the Centers for Medicare & Medicaid Services) publishes a decision tool at Are You a Covered Entity?
Who Is a Business Associate in New Jersey
Also federal. 160.103 defines a business associate as a person who, on behalf of a covered entity, "creates, receives, maintains, or transmits protected health information for a function or activity regulated by this subchapter, including claims processing or administration, data analysis, processing or administration, utilization review, quality assurance, patient safety activities listed at 42 CFR 3.20, billing, benefit management, practice management, and repricing." Billing companies, EHR vendors, cloud hosts, IT firms with system access, answering services, shredding companies, and their subcontractors. Each needs a signed BAA (Business Associate Agreement); the BAA guide covers the required terms. New Jersey's breach statute does not use the term; it applies to any "business," however organized, that holds residents' personal information, with or without a BAA
Key HIPAA rules and NJ specifics
Three federal rules apply to every New Jersey covered entity and business associate: the Privacy Rule (uses, disclosures and patient rights for PHI, protected health information), the Security Rule (safeguards for electronic PHI), and the Breach Notification Rule. HHS OCR HIPAA guidance covers all three. The HHS Office for Civil Rights enforces them; the state does not.
New Jersey has no single comprehensive health privacy code the way California or Texas does. It has narrower statutes, and each adds something the federal rule does not require.
The Identity Theft Prevention Act (N.J.S.A. 56:8-161 to 56:8-166)
Enacted as P.L.2005, c.226 and effective January 1, 2006, this is the state's breach notification and data-handling law. Three provisions apply to every practice, breach or no breach:
- Record destruction (56:8-162). Records containing personal information that are no longer retained must be destroyed "by shredding, erasing, or otherwise modifying the personal information in those records to make it unreadable, undecipherable or nonreconstructable through generally available means." A disposal standard with the force of state law, and it applies to paper.
- Social Security number handling (56:8-164). No entity may publicly post an individual's Social Security number, print it on a mailed document unless law requires it, print it on any card used to access services, require it to be sent over an unsecured internet connection, or use it alone as a website login.
- Breach notification (56:8-163). Covered in its own section below.
The statute's definition of personal information is narrower than HIPAA's definition of PHI (Protected Health Information). Under the original law, it meant a first name or initial and last name linked with a Social Security number, a driver's license or state identification number, or an account or card number with the code that would permit access to the account. A 2019 amendment (P.L.2019, c.95) added one more item to the list: a username or email address plus the password, or security question and answer, that would open an online account. A clinical note with no identifier from that list is PHI under HIPAA and not "personal information" under the New Jersey act. A billing file with Social Security numbers is both.
The New Jersey Data Privacy Act (N.J.S.A. 56:8-166.4 et seq.)
P.L.2023, c.266 was approved January 16, 2024 and took effect on the 365th day after enactment, which put it in force in January 2025. Section 10 states that nothing in the act "shall apply to" "protected health information collected by a covered entity or business associate subject to the privacy, security, and breach notification rules" of 45 CFR Parts 160 and 164.
Read that carefully. It exempts the data, not the organization. Website analytics, an email list, or a marketing pixel aimed at people who are not patients is personal data that is not PHI, and the act's thresholds (personal data of at least 100,000 consumers, or 25,000 consumers plus revenue from selling personal data) decide whether the act reaches it. Most solo practices fall below the thresholds; groups with a marketing arm should ask counsel. The Attorney General has "sole and exclusive authority" to enforce the act, and it creates no private right of action.
HIV Records and Record Retention
New Jersey's AIDS Assistance Act (N.J.S.A. 26:5C-5 and following) restricts disclosure of HIV-related records beyond HIPAA's treatment, payment, and operations permissions, generally requiring written consent outside listed exceptions. This guide does not quote that statute, so treat this as a flag: if the practice tests for or treats HIV, the consent form needs a New Jersey-specific review by counsel.
Retention is a state matter too. HIPAA sets no retention period for the chart itself; it requires that policies and required documentation be kept for "6 years from the date of its creation or the date when it last was in effect, whichever is later" (45 CFR 164.316(b)(2)(i) and 164.530(j)(2)). For hospitals, the New Jersey Department of Health's patient rights summary says a patient may obtain a copy of their medical records "for a reasonable fee within 30 days after submitting a written request to the hospital." The Board of Medical Examiners regulation (N.J.A.C. 13:35-6.5) sets the physician record period, commonly cited as seven years; confirm the current figure with the board before writing a retention schedule. The record retention guide covers the federal-versus-state split.
Conducting risk assessments and security steps
A risk assessment (a documented review of where ePHI lives and what could compromise it) is required of every covered entity and business associate by 45 CFR 164.308(a)(1)(ii)(A). HHS OCR's guidance on risk analysis describes the method; NIST SP 800-66 Rev. 2 walks through it step by step.
- Encryption (scrambling data so only key holders can read it): addressable under 164.312(a)(2)(iv), and in New Jersey it matters twice. The state breach statute only applies when access "has not been secured by encryption," and encrypted data that meets HHS guidance is not "unsecured PHI" under the federal rule.
- Access controls (limits on who can open which records): unique logins, no shared front-desk accounts, and prompt removal of former staff (164.312(a)(1)).
- BAAs (Business Associate Agreements): signed before any vendor touches PHI, with the state's "immediately following discovery" notice term written in (164.504(e)).
- Documentation: policies, the risk assessment and training records kept for six years (164.316(b)(2)(i)).
Breach reporting & state notifications
The federal rule first. 45 CFR 164.404(b) requires notice to affected individuals "without unreasonable delay and in no case later than 60 calendar days after discovery of a breach." Under 164.408(b), a breach involving 500 or more individuals goes to HHS "contemporaneously" with the individual notice; under 164.408(c), smaller breaches are logged and reported "not later than 60 days after the end of each calendar year." Under 164.406(a), a breach involving "more than 500 residents of a State or jurisdiction" also goes to prominent media serving that state. A business associate has the same 60-day ceiling to notify the covered entity (164.410(b)).
Now the state rule, N.J.S.A. 56:8-163. A business that "compiles or maintains computerized records that include personal information, shall disclose any breach of security of those computerized records following discovery or notification of the breach to any customer who is a resident of New Jersey whose personal information was, or is reasonably believed to have been, accessed by an unauthorized person." Four features distinguish it from HIPAA:
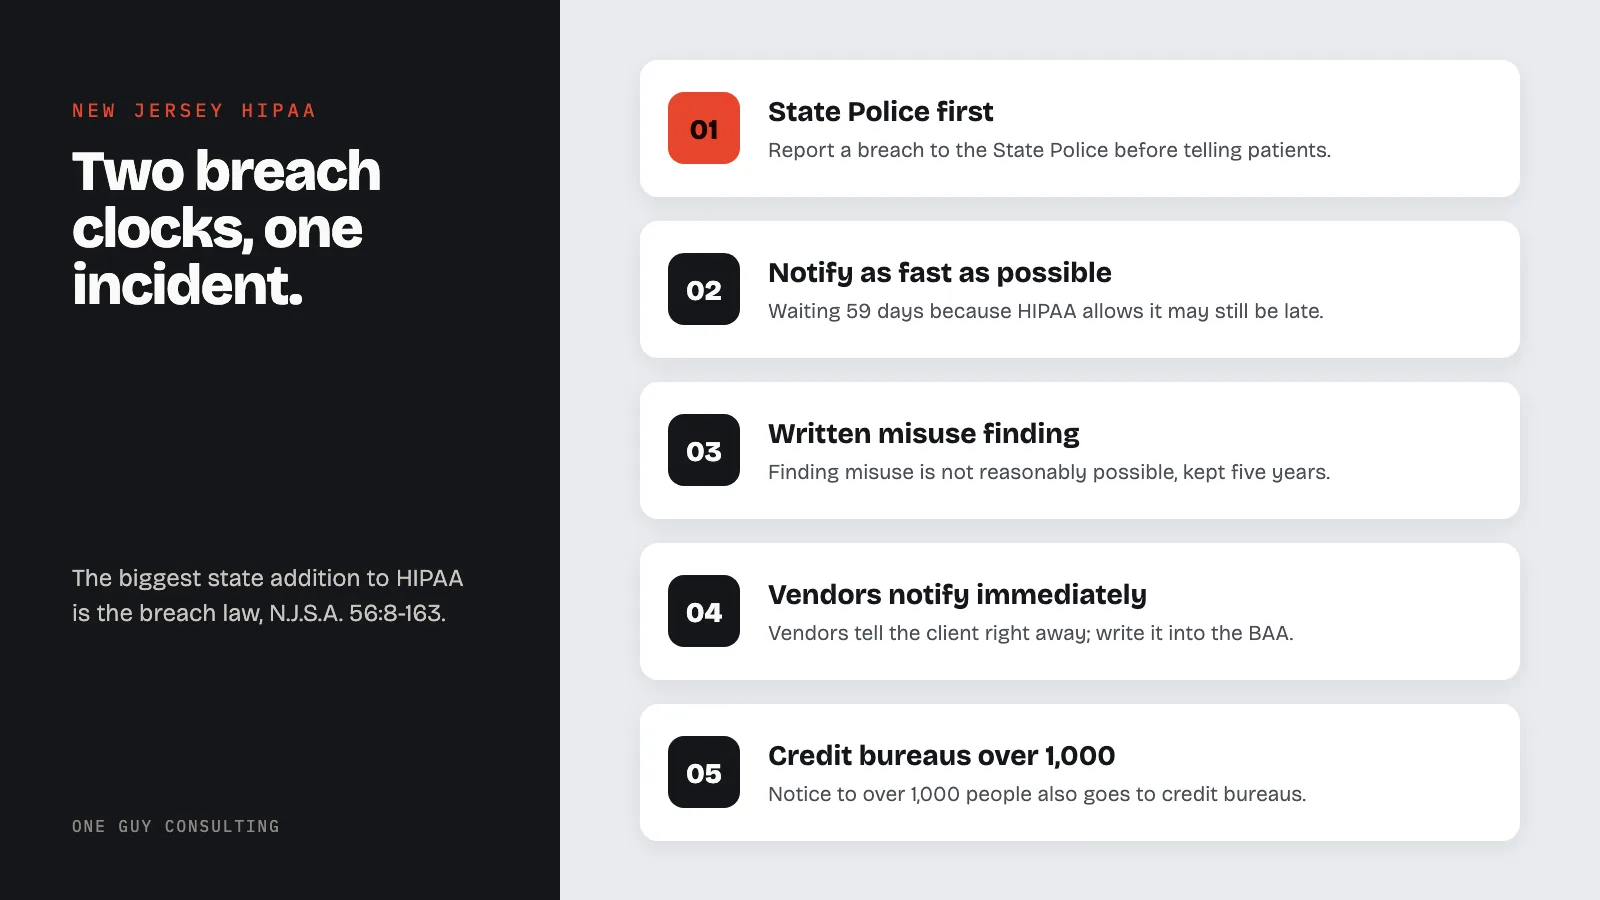
- No fixed day count. Disclosure must be made "in the most expedient time possible and without unreasonable delay." There is no 60-day ceiling to lean on. A practice that waits 59 days because HIPAA allows it may still be late under state law.
- State Police first. There is no numeric threshold; the duty attaches to every notifiable breach (quoted below). The state's cybersecurity cell, the NJCCIC, maintains data breach response resources for reporting.
- A documented misuse determination. Disclosure is not required "if the business or public entity establishes that misuse of the information is not reasonably possible. Any determination shall be documented in writing and retained for five years." That is a separate analysis from HIPAA's four-factor risk assessment in 164.402, with a different question and its own retention period.
- Vendors and credit bureaus. A business that maintains records "on behalf of another business" must notify that business "immediately following discovery," faster than HIPAA's 60-day ceiling and worth writing into the BAA A breach requiring notice to "more than 1,000 persons at one time" also requires notice to the nationwide consumer reporting agencies.
"Any business or public entity required under this section to disclose a breach of security of a customer's personal information shall, in advance of the disclosure to the customer, report the breach of security and any information pertaining to the breach to the Division of State Police in the Department of Law and Public Safety for investigation or handling, which may include dissemination or referral to other appropriate law enforcement entities."
(N.J.S.A. 56:8-163(c)(1), P.L.2005, c.226)
The state definition of breach of security is "unauthorized access to electronic files, media or data containing personal information that compromises the security, confidentiality or integrity of personal information when access to the personal information has not been secured by encryption or by any other method or technology that renders the personal information unreadable or unusable."
| Obligation | Federal HIPAA | New Jersey (N.J.S.A. 56:8-163) |
|---|---|---|
| Trigger | Breach of unsecured PHI (164.402) | Unauthorized access to unencrypted computerized "personal information" |
| Individual notice deadline | No later than 60 calendar days after discovery | Most expedient time possible; no fixed day count |
| Government notice | HHS: contemporaneous if 500 or more; annual log if fewer | Division of State Police, before customer notice, every breach |
| Media | Prominent outlets if more than 500 residents of a state | Only as substitute notice when direct notice is impractical |
| Credit bureaus | Not required | Nationwide agencies if more than 1,000 persons |
| Vendor to client | No later than 60 days (164.410) | Immediately following discovery |
| No-notice determination | Four-factor risk assessment (164.402) | Written finding that misuse is not reasonably possible, kept five years |
The working rule for a New Jersey practice: run the federal breach process from the breach notification guide, and add two lines. Line one: report to the State Police before any letter is mailed. Line two: mail as soon as the facts are known, not on day 59.
HIPAA Penalties in New Jersey
Federal OCR Penalty Tiers
45 CFR 160.404 sets four culpability tiers, and the dollar amounts are inflation-adjusted each year at 45 CFR 102.3. Under the 2025 adjustment, the per-violation ranges are: $145 to $73,011 where the entity did not know and could not reasonably have known; $1,461 to $73,011 for reasonable cause; $14,602 to $73,011 for willful neglect corrected within 30 days; and $73,011 to $2,190,294 for willful neglect not corrected. The calendar-year cap for identical violations is $2,190,294. OCR has also applied a Notice of Enforcement Discretion with lower annual caps for the first three tiers; those figures are not quoted here. Recent OCR case titles show the pattern: a $950,000 settlement over Security Rule failures (July 1, 2024), a $3,000,000 phishing settlement with Solara Medical Supplies (January 14, 2025), and a $600,000 phishing settlement with a health care network (April 23, 2025). The penalty amounts post tracks the numbers.
New Jersey Attorney General Enforcement
N.J.S.A. 56:8-166 makes it "an unlawful practice and a violation of" the Consumer Fraud Act (N.J.S.A. 56:8-1 et seq.) to "willfully, knowingly or recklessly violate" the breach notification, record destruction, and Social Security number sections. The office uses those tools. In May 2023 the New Jersey Attorney General co-led a $2.5 million multistate settlement with EyeMed over a data breach the office said compromised the personal and medical information of approximately 2.1 million people, more than 52,000 of them in New Jersey, in violation of state law and HIPAA. Patients cannot sue under HIPAA itself (HIPAA gives them no private right of action). They still sue after breaches, often for negligence. That risk sits outside HHS enforcement.
HIPAA Compliance for New Jersey Healthcare Providers
New Jersey Hospitals and Health Systems
Large systems already run federal programs. The state layer shows up in three places: the State Police report step in the incident response plan, the Social Security number rules in patient-facing documents and portals, and vendor contracts, which should carry the state's "immediately following discovery" notice term. Hospitals that treat HIV also need the AIDS Assistance Act consent workflow reviewed by counsel.
New Jersey Dental Practices
Dental offices are covered entities the moment they submit an electronic claim; the dental compliance page covers the federal program. The New Jersey additions are practical: intake forms with a Social Security number cannot come back on a postcard, retired paper charts must be shredded rather than bagged, and a lost unencrypted laptop with patient financial data triggers the State Police report. The OCR case against a dental practice for social media disclosures of patients' PHI ($10,000, October 2, 2019) is a reminder that dental violations usually start with a review reply, not a hacker.
New Jersey Behavioral Health Providers
For most New Jersey behavioral health practices the federal rules do the heavy lifting: psychotherapy notes have their own protection under HIPAA, substance use disorder records may fall under 42 CFR Part 2, and the OCR penalty against a mental health center for failing to provide timely access to records ($100,000, November 19, 2024) shows where enforcement lands. State confidentiality provisions for psychiatric facility records exist and should be checked with counsel. The behavioral health compliance page covers the program.
New Jersey Home Health and Long-Term Care
Home health agencies and nursing facilities carry long vendor lists and a workforce that moves patient data on phones and in cars. Each vendor needs a BAA; each device needs encryption. That generally keeps a lost phone out of both breach statutes. The 2024 OCR penalty against a New Jersey nursing facility for failing to provide timely access to records is the local warning: the 30-day access deadline in 45 CFR 164.524(b)(2) applies to a nursing home exactly as it applies to a hospital.
New Jersey HIPAA Compliance Checklist
| Requirement | Source | Timing | Evidence to keep |
|---|---|---|---|
| Security risk analysis and risk management plan | Federal, 164.308(a)(1) | Documented; reviewed at least annually in practice | Risk analysis report, remediation plan |
| Workforce training | Federal, 164.530(b), 164.308(a)(5) | New hires; when policies change; annual in practice | Training log with dates and names |
| Signed BAA with every PHI vendor | Federal, 164.504(e), 164.314(a) | Before access; add the state "immediately" notice term | Executed agreement per vendor |
| Breach procedure with a State Police report step | Federal 164.404 to 164.410; N.J.S.A. 56:8-163(c) | State Police before customer notice; letters without unreasonable delay | Incident log, report confirmation, notice copies |
| Written no-notice determination, if relied on | N.J.S.A. 56:8-163(a) | At the time of the decision | Signed memo, kept five years |
| Record destruction and Social Security number handling | N.J.S.A. 56:8-162, 56:8-164; federal 164.310(d) | Ongoing; review forms and portals annually | Written policy, shredding certificates, form inventory |
| Medical record retention schedule | State licensing board rule | Per board rule | Written retention schedule |
One note on timing. The proposed update to the HIPAA Security Rule, published in January 2025, would add express requirements such as encryption and multifactor authentication. It is a proposal, not current law, and OCR is not enforcing it. Nothing in this guide depends on it.
FAQ
What does this page cover?
An overview of HIPAA compliance requirements in New Jersey for practice and office managers.
Who should read this?
Practice managers, office managers, and practitioners in New Jersey seeking HIPAA guidance.
How can One Guy Consulting help?
One Guy Consulting provides a HIPAA compliance and cybersecurity SaaS solution for healthcare entities.
Where to find official rules?
See HHS Office for Civil Rights and New Jersey official health agencies for the primary guidance.
How One Guy Consulting helps
The federal program comes first: risk analysis, written policies, workforce training, and signed BAAs. The New Jersey layer is a short addendum to the breach procedure plus a few state-specific consent and retention checks. One Guy Consulting's Full-Scope plan ($1,300 a year, or $120 a month, flat rate per location) includes 4 hours a month of 1:1 implementation calls with Chuck. Start with a free 30-minute intro call. No obligation, no pressure.
Client example (anonymized; a single-location practice, not in New Jersey): before its review, several vendors were touching PHI with no BAA in place. After it, every missing BAA was signed and the practice had a vendor review it can run again. Read case 05.
Sources
- HHS Office for Civil Rights: HIPAA for professionals
- New Jersey Department of Health: Your Rights as a Patient
- CMS: Are You a Covered Entity?
- NJCCIC: Data Breach Prevention, Response, and Resources
- NIST SP 800-66 Rev. 2
- P.L.2005, c.226, Identity Theft Prevention Act (N.J.S.A. 56:8-161 to 56:8-166), New Jersey Legislature
- P.L.2023, c.266, New Jersey Data Privacy Act (N.J.S.A. 56:8-166.4 et seq.), New Jersey Legislature
- New Jersey Attorney General: $2.5 million multistate EyeMed data breach settlement (May 16, 2023)
- 45 CFR 160.203 (preemption of state law)
- 45 CFR 160.103 (definitions: covered entity, business associate)
- 45 CFR 164.404 (breach notification to individuals)
- 45 CFR 164.408 (breach notification to the Secretary)
- 45 CFR 102.3 (civil money penalty amounts)
- HHS: Breach Notification Rule
Related Reading
- HIPAA compliance requirements in New York
- Illinois HIPAA compliance and requirements guide
- State privacy laws vs federal HIPAA requirements
- HIPAA Breach Notification Rule compliance guide
HIPAA compliance in other states
State law stacks on top of HIPAA differently in every state. These guides cover the statutes that move the baseline where you operate.
Try three One Guy Consulting 3D staff training courses free →