Business Associate Agreement FAQ
Vendors who create, receive, maintain, or transmit PHI (including ePHI) require a Business Associate Agreement (BAA); others usually do not. This FAQ describes which vendors qualify, required BAA provisions under 45 CFR 164.504(e)(2), and vendor-specific rules.
BAA Vendor Vetting: Who Needs One & What to Review
15 questions covering Business Associate definitions, specific vendor BAA requirements for Microsoft 365, Google Workspace, IT companies, shredding services, and more. Plus vendor vetting, review processes, and what to do when a vendor refuses to sign.
BAA Terms and Regulatory References
Business Associate: Under 45 CFR 160.103, a Business Associate is a person or entity that performs functions or activities for a covered entity. The work must involve access to Protected Health Information (PHI). This includes claims processing, data analysis, utilization review, billing, and legal, actuarial, accounting, consulting, or financial services.
Business Associate Agreement (BAA): A written contract required under 45 CFR 164.502(e) between a covered entity and a business associate. The agreement must set out the permitted and required uses and disclosures of PHI by the business associate. It must also give assurances that the business associate will safeguard the information.
Electronic Protected Health Information (ePHI): As defined in 45 CFR 160.103, ePHI is individually identifiable health information. It is transmitted by or maintained in electronic media. This includes patient records, billing data, and insurance information stored or sent electronically.
Vendor vs. Business Associate: A vendor is only a Business Associate if it creates, receives, maintains, or transmits PHI on behalf of a covered entity. A vendor that never accesses, handles, or stores PHI does not meet the definition of a Business Associate and does not require a BAA. More definitions are in the HIPAA compliance glossary.
What a BAA must include (45 CFR 164.504(e)(2))
A BAA must define permitted PHI uses, require safeguards and breach reporting, bind subcontractors, allow HHS review, and require PHI return or destruction at termination. The full list:
What a BAA must contain (45 CFR 164.504(e)(2)): The contract must establish the permitted and required uses and disclosures of PHI by the business associate, and must require the business associate to:
- not use or further disclose PHI other than as the contract permits or as required by law;
- use appropriate safeguards, and comply with the Security Rule for electronic PHI;
- report to the covered entity any use or disclosure not provided for by the contract, including breaches of unsecured PHI;
- ensure that any subcontractors that handle PHI agree to the same restrictions and conditions;
- make PHI available for patient access, amendment, and an accounting of disclosures (45 CFR 164.524, 164.526, 164.528);
- make its internal practices, books, and records available to HHS;
- at termination, return or destroy all PHI if feasible, or extend the contract's protections to it;
- and the contract must authorize the covered entity to terminate it if the business associate violates a material term.
Full text: eCFR 164.504(e)(2). HHS guidance: Business Associates FAQs and sample BAA provisions. Vendor BAA terms: Google Workspace BAA, Microsoft HIPAA/HITECH.
Business Associate Agreement FAQ
Who needs a BAA?
3 questions01What is a Business Associate?+
A Business Associate, as defined under 45 CFR 160.103, is a person or organization that works on behalf of a covered entity. The work must involve the use or disclosure of Protected Health Information (PHI). If the work involves creating, receiving, maintaining, or transmitting PHI, that entity is likely a Business Associate. If that describes your company, the business associate compliance guide covers your own HIPAA obligations.
02What is a Business Associate Agreement?+
A BAA is a written contract required under 45 CFR 164.502(e). Under this regulation, covered entities must obtain satisfactory assurances from their business associates that PHI will be appropriately safeguarded. The agreement establishes the permitted uses and disclosures of PHI and the responsibilities of each party.
The rule itself, in two sentences:
“A covered entity may disclose protected health information to a business associate and may allow a business associate to create, receive, maintain, or transmit protected health information on its behalf, if the covered entity obtains satisfactory assurance that the business associate will appropriately safeguard the information.”
“The satisfactory assurances required by paragraph (e)(1) of this section must be documented through a written contract or other written agreement or arrangement with the business associate that meets the applicable requirements of § 164.504(e).”
45 CFR 164.502(e)(1)(i) and (e)(2)
Learn more about One Guy Consulting's BAA management services.
03What's the biggest misconception about Business Associates?+
Many people think every vendor needs a BAA. That is not true. Being a vendor and being a Business Associate are not the same thing.
Vendor-specific rules: Microsoft 365, Google Workspace, IT, shredding
5 questions04Does Microsoft 365 require a Business Associate Agreement?+
It depends on how you use it. If Microsoft stores, sends, or handles your patient data (ePHI), then yes, you likely need a BAA with them. Microsoft includes its HIPAA BAA automatically for in-scope services on qualifying business and enterprise plans, through its Product Terms (Microsoft HIPAA/HITECH documentation). Confirm your plan and which services are covered before using Microsoft 365 with ePHI.
05Does Google Workspace require a Business Associate Agreement?+
If you use Google Workspace to store, send, or handle patient data, you should get a BAA from Google. Google provides a BAA for Google Workspace accounts, and an administrator must accept it in the Admin Console before using Workspace services with ePHI.
06Does an IT company require a Business Associate Agreement?+
In most cases, yes. An IT company with access to systems that hold ePHI meets the Business Associate definition under 45 CFR 160.103. That holds true even if it does not store patient data directly. Managed service providers, help desk vendors, and IT support companies often require a BAA.
07Does a shredding company require a Business Associate Agreement?+
Yes. A shredding company that handles records with PHI meets the Business Associate definition. It maintains or has access to PHI while destroying them. A BAA is required before the shredding company begins handling your records.
08Does a janitorial service require a Business Associate Agreement?+
Usually, no. A janitorial service does not often create, receive, maintain, or transmit PHI, so it generally does not meet the Business Associate definition. But if janitorial staff have unsupervised access to areas where PHI is stored or visible, practices should put physical safeguards in place. A confidentiality agreement may also help.
| Vendor | BAA needed? | Why |
|---|---|---|
| Microsoft 365 | Yes, if it stores, sends, or handles ePHI | Microsoft includes its BAA for in-scope services on qualifying plans through its Product Terms |
| Google Workspace | Yes, if used with PHI | An administrator must review and accept Google's BAA before using PHI in Google services (Google HIPAA compliance page) |
| IT company or managed service provider | In most cases, yes | Access to systems that hold ePHI meets the Business Associate definition in 45 CFR 160.103 |
| Shredding company | Yes | It maintains or has access to PHI while destroying records |
| Janitorial service | Usually, no | It does not often create, receive, maintain, or transmit PHI; use physical safeguards and consider a confidentiality agreement |
Vendor vetting checklist and processes
5 questions09How should businesses vet vendors?+
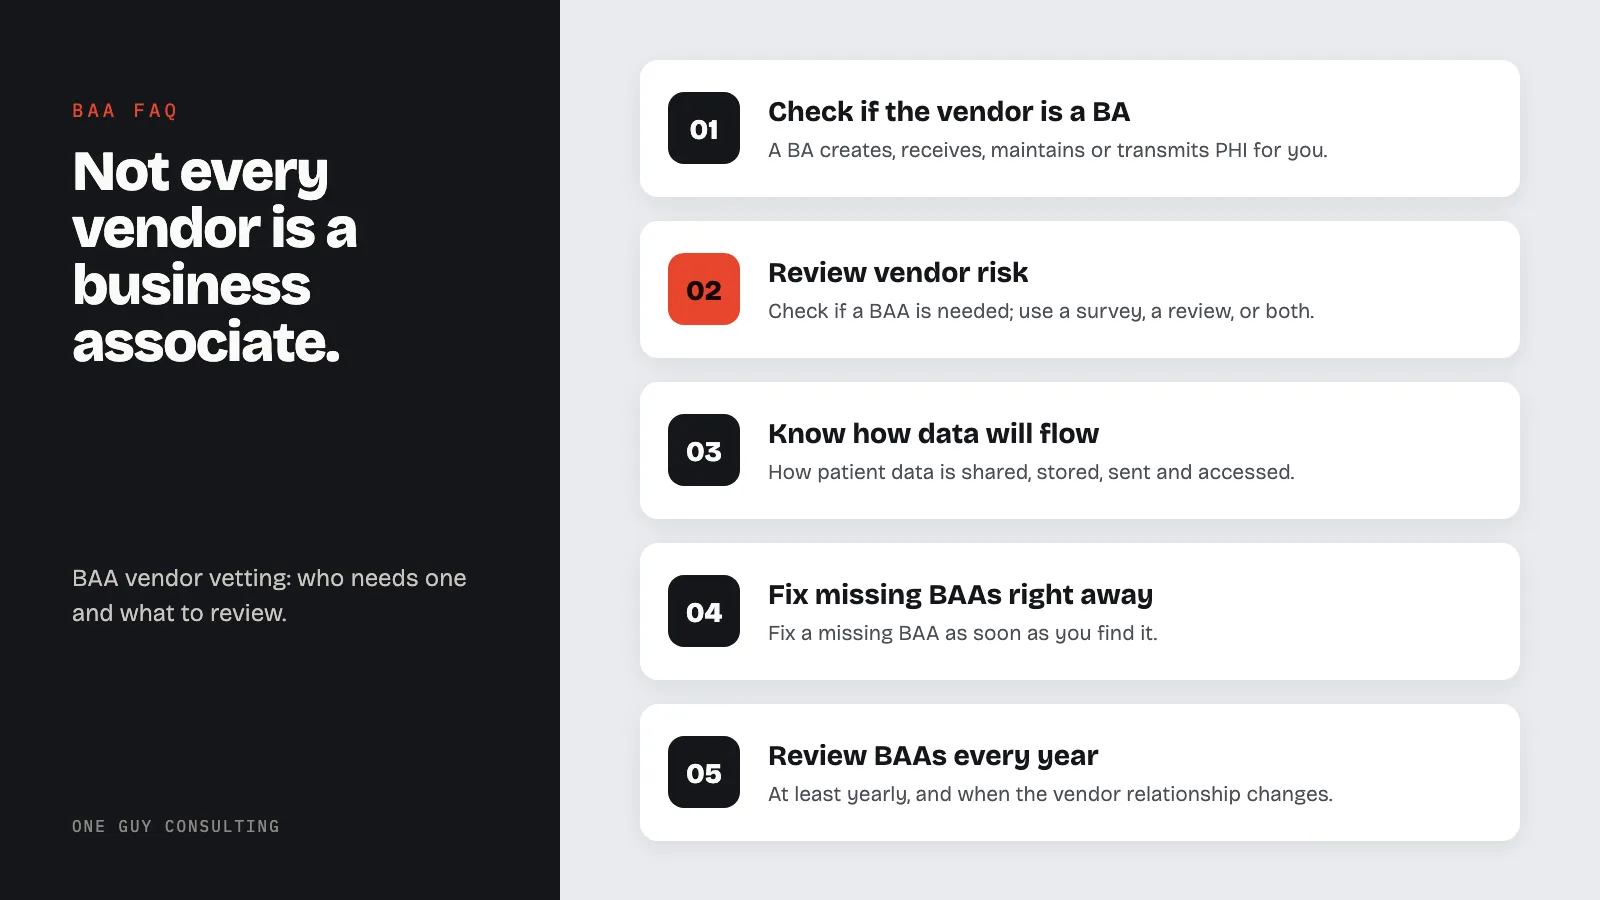
At a minimum, check if a BAA is needed and review vendor risk. Use a short survey, a security review, or both.
10What should be reviewed before signing a Business Associate Agreement?+
Know exactly how patient data will be shared, stored, sent, accessed, or released.
11What's the biggest vendor-management mistake healthcare businesses make?+
One of the biggest mistakes is failing to evaluate vendor risk.
12How often should BAAs be reviewed?+
HIPAA does not set a review interval for BAAs. Most practices review their BAAs once a year, and again when the vendor relationship changes in a material way, such as a shift in the scope of services, the types of PHI handled, or the vendor's security posture. Reviewing BAAs alongside periodic updates to your Security Risk Assessment (45 CFR 164.308(a)(1)(ii)(A)) keeps both current.
13What happens if a required BAA is missing?+
Fix a missing BAA as soon as you find it.
Example from my own work: I worked with a single-location practice that had put real work into its program, but a vendor review found several vendors handling PHI with no BAA in place.
- Before: several vendors touching PHI with no Business Associate Agreement; some agreements could not be found and others were never signed.
- After: every missing BAA signed, every vendor record in one place, and a check that runs on any new vendor before it gets near PHI.
Read the anonymized case study (Case 05). In another engagement, a Florida mental health franchise office with policies never written and a state auditor due in days was audit-ready in under a week and passed its state audit (Case 01).
What to do when a vendor refuses to sign
2 questions14Can a vendor refuse to sign a Business Associate Agreement?+
Yes. A vendor can decline to sign any agreement.
15What should a business do if a vendor won't sign a Business Associate Agreement?+
If the vendor is a business associate, you cannot share PHI with it without a BAA (45 CFR 164.502(e)). Stop sending it PHI, then either restructure the work so the vendor never touches PHI or move to a vendor that will sign.
No questions match that search. Try a shorter word, check the glossary, or ask Chuck directly.
One Guy Consulting helps practices inventory their vendors, determine which require BAAs, and manage the entire BAA execution process. Its vendor management service includes risk evaluation and ongoing monitoring.
One Guy Consulting in 37 seconds
New to us? This short video shows who we are and how we help small practices with HIPAA compliance.
Need Help Managing Your Business Associate Agreements?
Book a free 30-minute intro call. I will review your vendors with you, identify which ones need BAAs, and show you how I handle the whole process.