HIPAA Vendor Management for Healthcare Organizations
Any vendor that touches your patient data is your responsibility under HIPAA. This service inventories every vendor with PHI access, executes the required Business Associate Agreements, reviews each vendor's security practices, and keeps that oversight current.
Required under 45 CFR 164.502(e), 164.504(e), and 164.308(b)
What Is HIPAA Vendor Management?
What is HIPAA Vendor Management? The systematic identification, assessment, and ongoing oversight of all third-party vendors who access, store, or transmit PHI, as required under 45 CFR §164.502(e), §164.504(e), and §164.308(b).
Vendor management means knowing who handles your patient data and making sure they protect it. Every outside company that touches PHI (protected health information, any health data that can identify a patient), such as your EHR vendor, billing service, IT support or cloud storage, counts as a business associate. You need a plan to track them all. Those vendors carry HIPAA duties of their own; see our business associate compliance guide.
Three HIPAA Vendor Management Requirements
- Business Associate Agreement contracts: 45 CFR §164.502(e) requires covered entities to obtain satisfactory assurances from business associates that they will appropriately safeguard PHI. These assurances must be documented in a written BAA.
- BAA content requirements: 45 CFR §164.504(e) specifies what a BAA (Business Associate Agreement, the written contract HIPAA requires before a vendor can handle PHI for you) must contain, including permitted uses and disclosures of PHI, required safeguards, breach reporting obligations, and subcontractor requirements.
- Ongoing vendor oversight: 45 CFR §164.308(b) requires covered entities to implement policies and procedures for authorizing access to ePHI (electronic protected health information) by business associates and to monitor compliance with BAA terms over time.
“A covered entity may disclose protected health information to a business associate and may allow a business associate to create, receive, maintain, or transmit protected health information on its behalf, if the covered entity obtains satisfactory assurance that the business associate will appropriately safeguard the information.”
From 45 CFR §164.502(e)(1)(i), the HIPAA Privacy Rule standard for disclosures to business associates.
Vendor Risk Tiering
Not all vendors carry the same level of risk. Vendor risk tiering classifies each vendor based on the type and volume of PHI they access:
- Tier 1, Low Risk: Vendors with no direct PHI access or incidental exposure only (e.g., janitorial services with facility access, general IT hardware suppliers).
- Tier 2, Moderate Risk: Vendors with indirect or limited PHI access through system integrations or support functions (e.g., IT support providers, payment processors, cloud backup services).
- Tier 3, High Risk: Vendors with direct, persistent access to PHI through core systems (e.g., EHR vendors, billing companies, cloud-hosted practice management platforms). These vendors require the most thorough security assessments and the most detailed BAA terms.
If a vendor mishandles patient data, your organization faces the investigation and the fines. HIPAA holds covered entities responsible for their business associates' handling of PHI. Under 45 CFR §164.502(e), the covered entity must obtain satisfactory assurances: a signed BAA alone, without ongoing oversight, does not meet this standard.
Who Needs HIPAA Vendor Management?
HIPAA vendor management applies to any covered entity or business associate that shares PHI with third parties. If your organization matches any of the following, a structured vendor program is indicated:
- Organizations that cannot produce a complete list of all vendors with access to PHI
- Practices with unsigned, expired, or outdated Business Associate Agreements
- Growing teams adding new SaaS tools, cloud services, and integrations without a vendor review process
- Organizations that signed BAAs but have never assessed vendor security practices or breach history
- Business associates who subcontract PHI handling to downstream vendors without documented subcontractor BAAs
HIPAA Vendor Rules and What We Produce
Each vendor management rule, what it asks of your practice, and the deliverable that answers it.
| Rule | What it requires | What you receive |
|---|---|---|
| 45 CFR §164.502(e) | Satisfactory assurance, documented in a written BAA, that a business associate will appropriately safeguard PHI | Complete vendor inventory and BAA status report |
| 45 CFR §164.504(e) | BAA content: permitted uses and disclosures, required safeguards, breach reporting, and subcontractor terms | BAA review against these requirements, plus BAA templates and in-platform signing |
| 45 CFR §164.308(b) | Satisfactory assurances before a business associate creates, receives, maintains, or transmits ePHI (electronic PHI) for you | Vendor risk assessments and an ongoing monitoring framework |
Five-Step Vendor Management Process
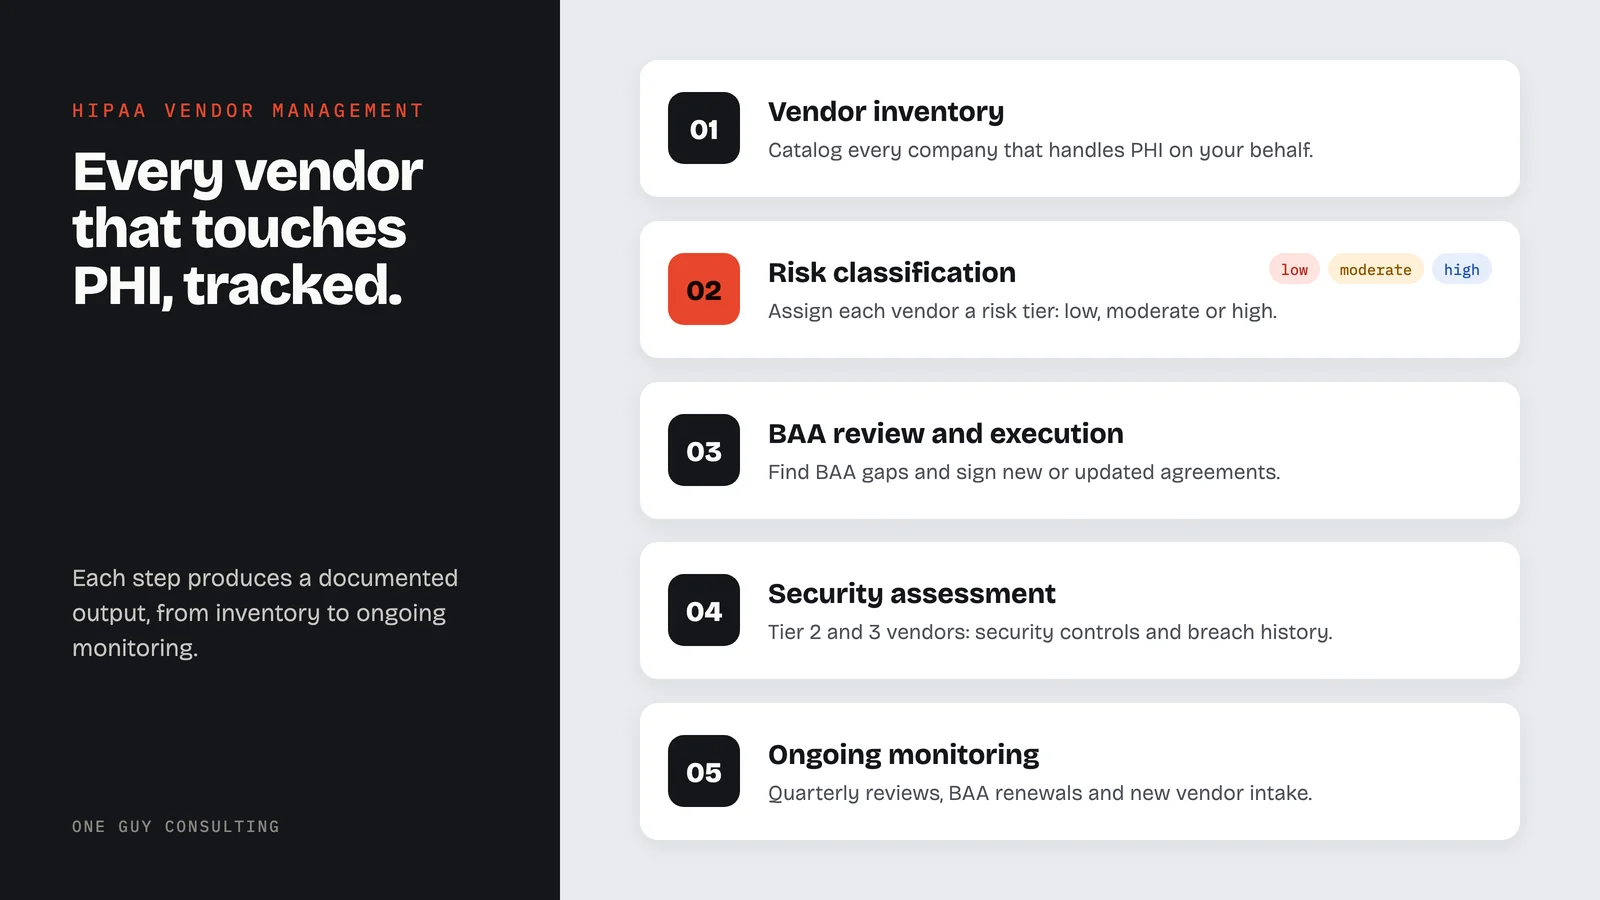
Each step produces a documented output that maps to specific HIPAA vendor management requirements under 45 CFR §164.502(e), §164.504(e), and §164.308(b).
- 01
Vendor Inventory
Identify and catalog every company that accesses, stores, or transmits PHI on your behalf. Include contractors, software vendors, cloud services, and service providers. Not sure which of them need a BAA? The Business Associate Agreement FAQ covers Microsoft 365, Google Workspace, IT companies, shredding services, and more.
OutputComplete vendor inventory with PHI access type, contact information, and business associate classification for each vendor. - 02
Risk Classification
Assign each vendor a risk tier (Tier 1 low, Tier 2 moderate, Tier 3 high) based on PHI volume, access type, storage method, and security posture.
OutputVendor risk register with risk tier assignment, PHI access mapping, and assessment priority ranking. - 03
BAA Review & Execution
Review all existing BAAs against §164.504(e) content requirements. Identify gaps and execute new or updated BAAs for all vendors that qualify as business associates.
OutputBAA status report showing compliant, expired, missing, and newly executed agreements. BAA templates provided for vendors that need them. - 04
Security Assessment
Evaluate each Tier 2 and Tier 3 vendor's security controls, breach history, incident response procedures, and subcontractor relationships.
OutputVendor security assessment results with risk ratings, subcontractor identification, and documented findings for each assessed vendor. - 05
Ongoing Monitoring
Establish a documented schedule for quarterly vendor reviews, BAA renewals, and new vendor onboarding. Trigger reassessment when a vendor changes services, reports a breach, or adds subcontractors.
OutputOngoing monitoring framework with quarterly review checklist, BAA renewal reminders, and new vendor intake process.
Case 05: Finding the Missing BAAs
A single-location practice relied on a long list of outside vendors. Several of them handled protected health information (PHI) with no Business Associate Agreement (BAA) in place.
Chuck sorted the vendor files, found which vendors handled PHI without a BAA, and chased down every missing agreement.
Every missing BAA was signed. The practice now has sorted vendor files and a written vendor review it can run again.
From our published case studies. Read Case 05 or read all six case studies.
Implementation Timeline
Most organizations finish their first vendor inventory and BAA review in weeks, not months. After that, monitoring folds into your regular compliance routine.
- Vendor discovery & inventory
- PHI access mapping
- Risk classification framework
- BAA review & gap identification
- BAA template preparation
- Execution tracking
- Vendor security assessments
- Subcontractor identification
- Risk register completion
- Quarterly vendor reviews
- BAA renewal tracking
- New vendor onboarding process
Timelines vary by vendor count and BAA gap volume. We scope each engagement before kickoff.
Vendor Patterns by Healthcare Specialty
Different practice types use different vendors. We tailor our approach to match how your practice actually works.
Medical Practices
EHR systems, labs, referral networks, billing companies, and clearinghouses all need BAAs.
Behavioral Health
Telehealth platforms, scheduling tools, and third-party note systems, all with extra sensitivity rules.
Dental Practices
Imaging vendors, practice management software, patient messaging tools, and dental cloud services.
Pharmacies
Medication systems, POS vendors, prescription delivery services, and wholesaler data links.
Business Associates
Your vendors have vendors too. BAA requirements flow downstream through every tier of the chain. See our HIPAA consulting for business associates.
Telehealth Providers
Video platforms, remote monitoring tools, and patient portal providers all need review.
What Your Vendor Program Includes
Complete Vendor Inventory
Every vendor listed with their PHI access type, risk level, BAA status, and contact info.
BAA Status Report
Clear report showing which vendors need BAAs, which BAAs need updates, and which are good.
Vendor Risk Assessments
Security questionnaire results and risk ratings for your high and moderate risk vendors.
BAA Templates
Ready-to-sign BAA templates for any vendor that still needs one.
Ongoing Monitoring Framework
Quarterly review schedule, BAA renewal reminders, and a checklist for adding new vendors.
In-Platform BAA Execution
BAAs are generated automatically. Both parties sign electronically inside the platform, and the signed document lives on the vendor's profile through the full six-year retention window.
Vendor management is included in Full-Scope.
One plan, three ways to pay. No per-user fees. Every client gets 4 hours a month of 1:1 implementation calls with Chuck.
- The full platform: SRA, gap analysis, remediation plans
- Policy templates and staff training
- Vendor and BAA management
- 4 hours a month of 1:1 implementation calls with Chuck
- Incident response guidance
- CMS audit response support
One payment, two full years of coverage.
Secure checkout by Stripe. Your payment details go straight to Stripe and never touch our servers.
Why This Approach Delivers Better Outcomes
A signed BAA is a contract, not a security control. Under 45 CFR §164.308(b), covered entities must implement policies and procedures for authorizing and overseeing business associate access to ePHI. Signing a BAA without assessing the vendor's security does not satisfy this requirement.
Documented vendor assessments serve as evidence of due diligence during HHS investigations. The Telnyx supply chain incident demonstrated how one vendor failure can expose an entire customer base. Organizations with documented assessments and current BAAs can demonstrate they met their oversight obligations under HHS enforcement standards.
Business associate breaches account for a significant portion of incidents on the HHS Breach Portal (see HHS Breach Notification Rule guidance). Under 45 CFR §164.502(e), the covered entity bears responsibility for obtaining satisfactory assurances that vendors will safeguard PHI. Ongoing oversight is the mechanism for verifying those assurances remain valid.
Common Pitfalls We Help You Avoid
- BAA-only approach: A signed BAA without a security assessment does not satisfy the oversight requirements of 45 CFR §164.308(b)
- Incomplete inventory: Most practices miss 40–60% of their vendors. SaaS tools and sub-processors are easy to overlook
- Stale BAAs: A BAA that has not been reviewed in years may not meet current HIPAA rules
- No subcontractor visibility: Your vendor's vendors need BAAs too. The chain does not stop at tier one
- One-time assessment: Vendor security changes over time. You need to reassess at least once a year
How to Track Vendor Compliance Progress
Track four numbers each quarter: How many vendors are on your list? How many have current BAAs? How many have passed a risk check? How many subcontractors are documented?
Flag any vendor that changed their services, had a breach, or has a BAA coming up for renewal. These are your triggers to reassess between annual reviews.
Vendor inventories lose accuracy as new tools are added, contracts expire, and vendors change their own subcontractors. Without regular updates, your documentation no longer reflects your actual vendor environment.
Quarterly reviews identify new gaps before they accumulate. 45 CFR §164.308(b) requires ongoing oversight of business associate relationships. A vendor inventory that goes unreviewed for a year creates a documented compliance gap.
Frequently Asked Questions
What is a Business Associate Agreement?+
How do I know which vendors need a BAA?+
Is signing a BAA enough for compliance?+
What about subcontractors of our vendors?+
How often should we review our vendor relationships?+
Ready to Take Control of Your Vendor Risk?
We will list your vendors, find BAA gaps, check security practices, and set up ongoing tracking so nothing slips through.
One Guy Consulting in 37 seconds
About the Author
Chuck Weiselberg. Zero clients fined. Zero failed audits.
Founder and HIPAA Consultant at One Guy Consulting, consulting since 2015. Chuck has held roughly 23,000 meetings with more than 3,500 organizations. Vendor and BAA management is part of Full-Scope, and clients work directly with him, not a ticket queue. Read Chuck’s full bio.
Deep-Dive Resources
These guides connect vendor management to the rest of your HIPAA program:
Explore our other HIPAA services
Questions About Vendor Management?
Tell us about your situation or question.
Or email us at hello@oneguyconsulting.com
Book Your Free 30-Minute Intro Call