Small Clinic HIPAA Starter Checklist
28 action items across 5 phases. Built for small clinics starting HIPAA compliance from scratch: no risk assessment, no written policies, no compliance program yet. Print it, check items off, build your evidence binder.
How to use this checklist
This checklist helps small clinics start HIPAA compliance when no SRA or written policies exist. Follow the phases in order. Each item tells you what document to keep as evidence. Start with the Security Risk Assessment so policies reflect identified risks.
"The Security Risk Assessment comes first because your policies should be informed by the risks you identify, not the other way around."
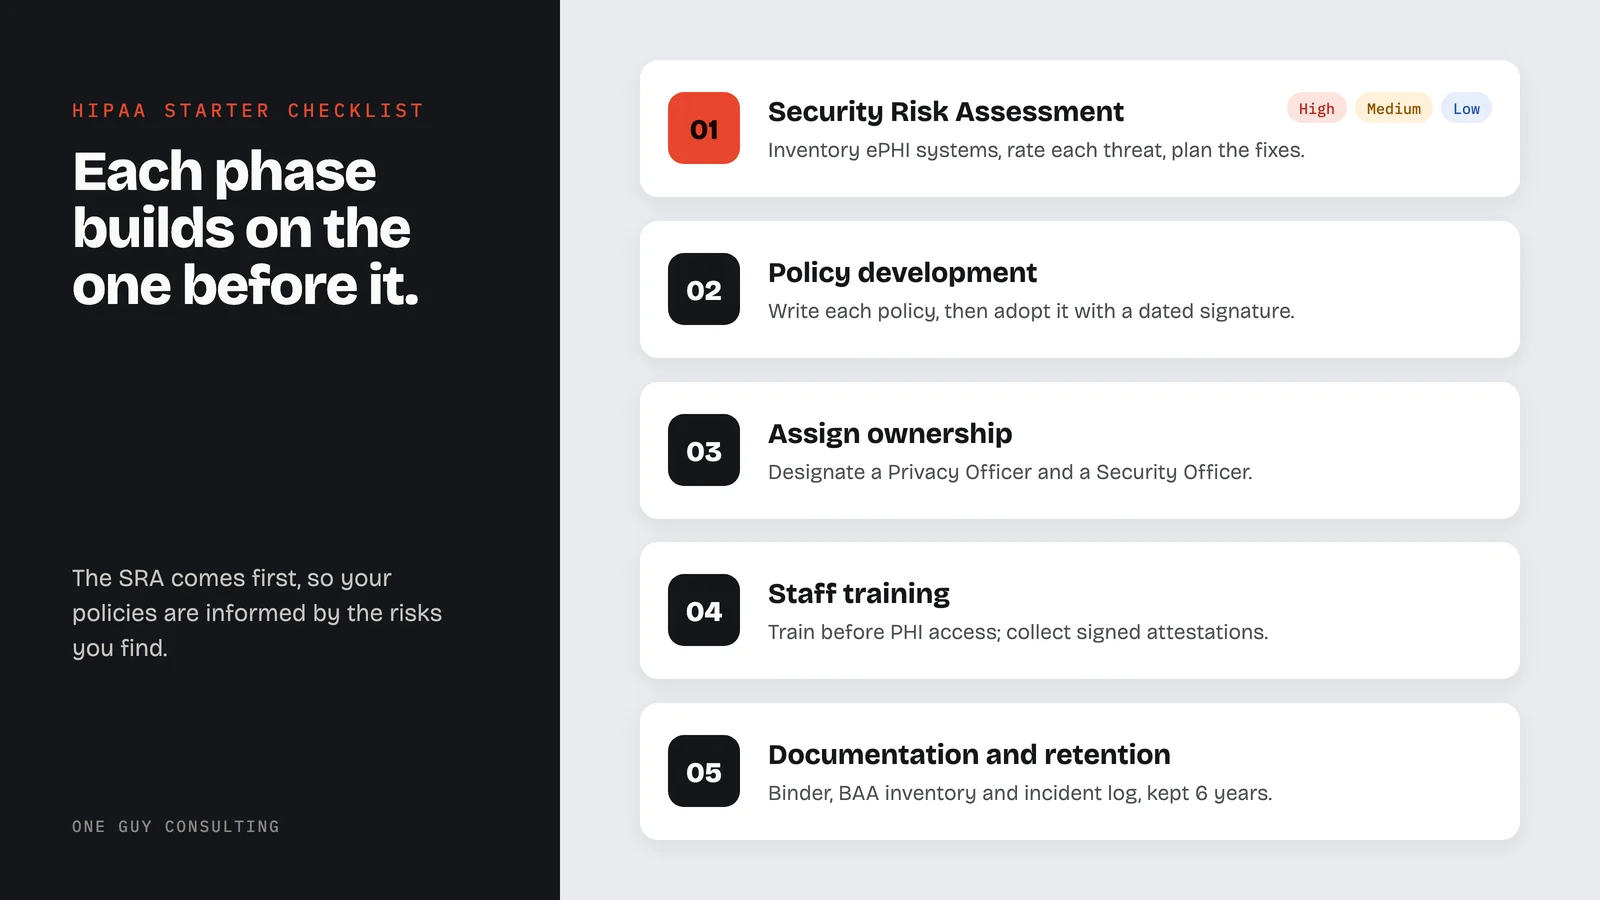
Each phase builds on the one before it. Skipping ahead creates gaps that are commonly cited as compliance findings.
This checklist covers the minimum required actions. It does not replace a comprehensive compliance program, but it closes the two highest-impact gaps identified in OCR enforcement actions: (1) no documented risk assessment and (2) no written policies.
Phases at a glance
Phase 1, Security Risk Assessment (5 items); Phase 2, Policy Development (11); then Assign Ownership, Staff Training, and Documentation and Retention. Each phase builds on the one before it.
Tick items as you go. Your progress stays in this browser only.
Security Risk Assessment (SRA)
RuleRequired by 45 CFR 164.308(a)(1)(ii)(A). Most commonly cited deficiency in OCR enforcement actions.
Policy Development
RuleRequired by 45 CFR 164.316(a). Policies must reflect your actual operations. Generic templates do not satisfy the requirement without customization.
Assign Ownership
RulePrivacy Officer required by 45 CFR 164.530(a)(1). Security Officer required by 45 CFR 164.308(a)(2).
Staff Training
RuleRequired by 45 CFR 164.308(a)(5)(i). OCR does not accept verbal-only training. Signed attestations are the minimum standard.
Documentation and Retention
RuleRetention required by 45 CFR 164.530(j). Six years from date of creation or date last in effect, whichever is later.
After you finish: next steps and maintenance
Completing this checklist gives your clinic a defensible compliance baseline. It does not make you "done." HIPAA compliance is an ongoing obligation. After completing all 28 items, your next priorities are:
- Review and update your SRA annually (or when significant changes occur)
- Review and update policies annually
- Deliver annual refresher training to all workforce members
- Monitor for security incidents and document your response
- Update your BAA inventory when vendors change
Starter checklist FAQ
Who is this checklist for?
Small clinics starting HIPAA compliance from scratch with no SRA and no written policies.
How many items and phases?
28 action items across 5 phases, completed in order.
How long must records be retained?
Retain records for six years from creation or date last in effect.
Does this replace a full compliance program?
No; it covers minimum required actions and closes two common OCR gaps: no SRA and no written policies.
Case example (anonymized): a mental health franchise office in Florida had no program in place, with a state auditor due in days. It got audit-ready in under a week, passed its state audit, and kept seeing patients. Read case 01.
References
Every item, done with you, not handed to you.
One Guy Consulting offers guided help to complete each checklist item with your staff, including the SRA, customized policies, and documented training. No software to figure out on your own.